Cybersecurity Awareness Month Week 1 – Passwords
Click to view full screen
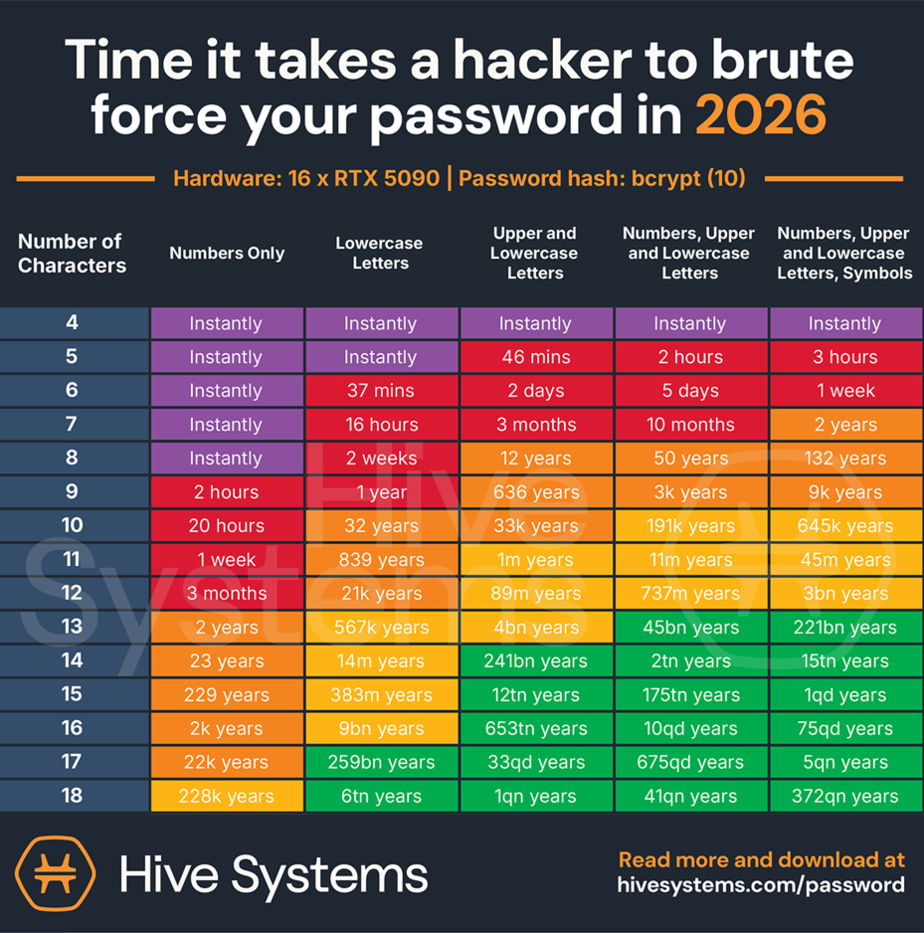
Did You Know…. An 8-character password can be cracked in seconds, no matter how many symbols you add. A complex 16-character password could take billions of years. Hackers don’t have that kind of time.
Protect yourself and your accounts using these 3 rules of strong passwords:
- Long Passwords are the Most Secure!
Your passwords should be at least 16 characters long. Length significantly increases the time it takes attackers to guess a password using automated tools. Short passwords – even complicated-looking ones – can be cracked quickly if they are less than 16 characters long. It is a difference of hours and days to millions of years for 16-character passwords. Longer passwords slow attackers down so much that most will give up and move on. - Every Account Needs a Unique Password
Each account should have its own password. No exceptions! Reusing passwords is incredibly common, so don’t beat yourself up if you’ve done it. But here’s the risk: if one account is breached, attackers will try that same password everywhere else (software and AI can help them do this). Email, banking, social media…everything becomes vulnerable when you reuse passwords - Make Each Password Random and Unrecognizable
Strong passwords are random strings of letters, numbers, and symbols. Avoid recognizable words, names, keyboard patterns, or dates. Complexity matters less than length and randomness. A long, random password is far stronger than a short, “clever” one with substitutions like P@ssw0rd!.
Want to test your password strength? Try this Password Strength Testing Tool. Want to learn more and improve your security posture? Reach out to a member of the BMT security team.

Leave A Comment